
Asus patches router flaws in VPN file imports and Telnet access
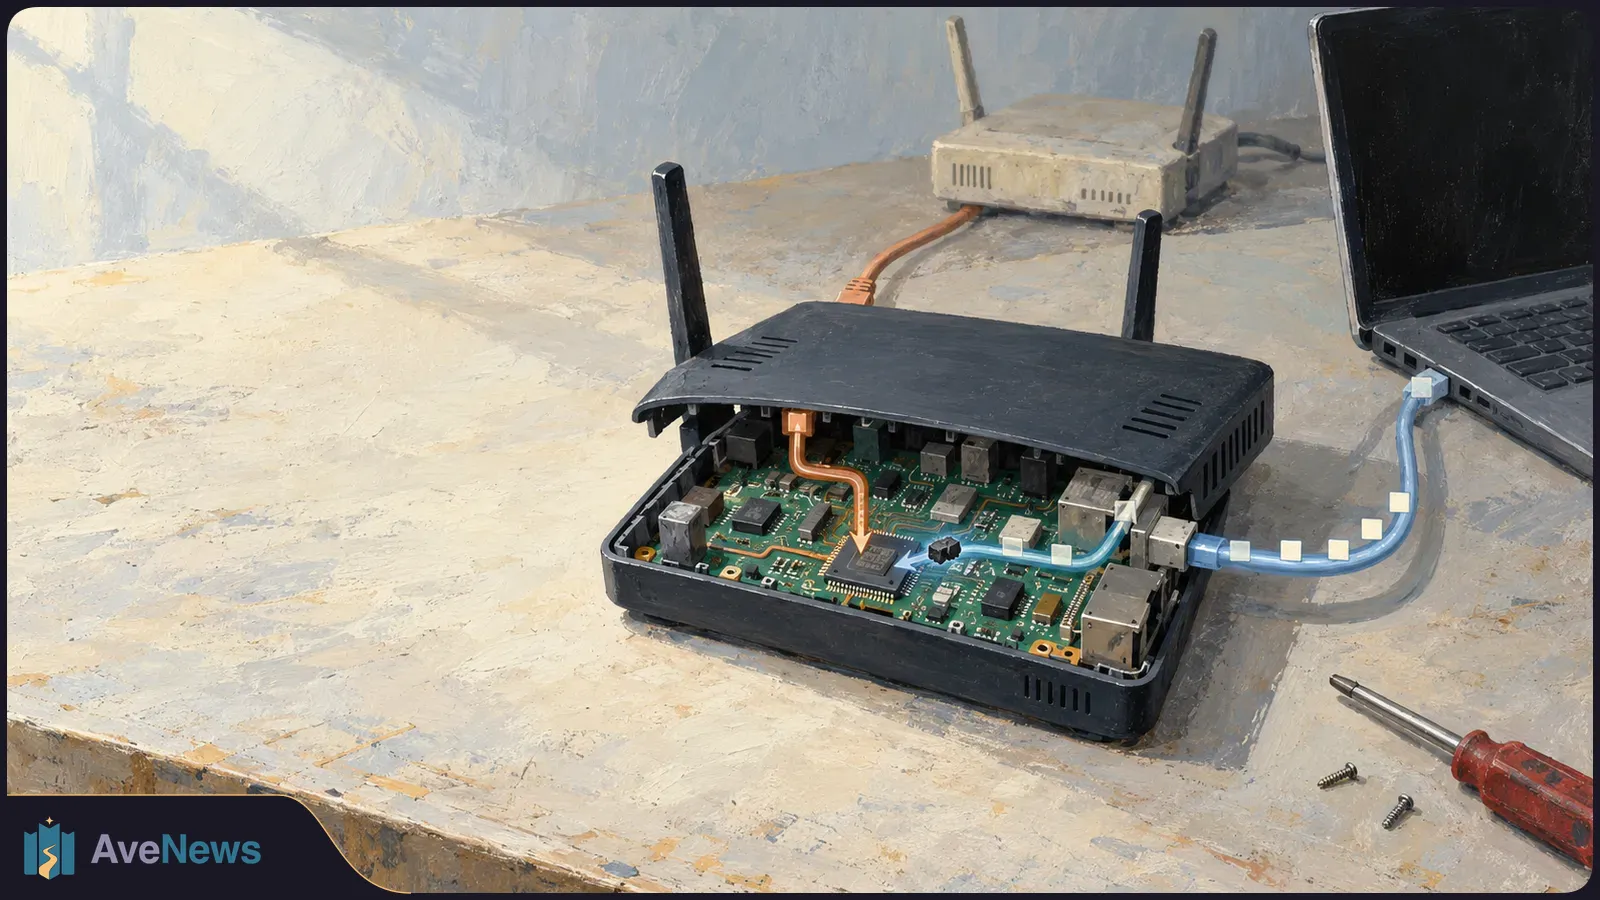
One flaw involves malicious configuration files imported into a router. The other may let a logged-in attacker run commands with full administrator privileges.
One flaw involves malicious configuration files imported into a router. The other may let a logged-in attacker run commands with full administrator privileges.
Asus has patched two router vulnerabilities that could let attackers run commands on the devices, according to Tom’s Hardware. One concerns imported VPN configuration files; the other may allow a logged-in attacker to gain full administrator privileges, potentially affecting devices connected to the router.
Asus identifies affected firmware series—the router’s built-in software—rather than router models. The severity scores below are Asus’s ratings, as reported by Tom’s Hardware, on the Common Vulnerability Scoring System (CVSS) 4.0 scale, which measures vulnerability severity out of 10.
| Vulnerability | CVSS 4.0 score | Affected firmware series |
|---|---|---|
| CVE-2026-14157: VPN configuration import | 9.4/10; rated critical | 3.0.0.6_102 |
| CVE-2026-13313: Telnet access | 8.9/10 | 3.0.0.6_102, 3.0.0.4_386 and 3.0.0.4_388 |
An Asus router can act as a virtual private network (VPN) client, connecting to a VPN provider using settings supplied in a configuration file. The VPN-file flaw concerns importing that file into the router itself through its web management interface. It does not concern ordinary use of VPN apps on a phone or laptop.
A user or a logged-in attacker can upload a maliciously crafted file through that interface. Tom’s Hardware describes the problem as text inside the file being read as formatting instructions rather than plain data, potentially allowing an attacker to run commands on the router.
The separate Telnet flaw involves diagnostic code left active in the firmware. It lets a logged-in attacker bypass security checks and enable Telnet, a service for accessing a device’s command line over a network. The attacker may then be able to run commands with root privileges—the highest level of administrator access—potentially affecting connected devices.
Tom’s Hardware directs potentially affected owners to firmware updates on Asus’s support page or their router’s product page. The exact fixed version for each router and whether either vulnerability is being actively exploited are not yet clear.
Asus also recommends importing VPN configuration files only from trusted sources and using a strong, unique administrator password. Its reported guidance calls for at least 10 characters, with a mix of uppercase letters, numbers and symbols. The company advises against running untrusted scripts, tools or commands on any device within the local network and warns that attackers may trick administrators into taking unsafe actions.
Routers that have reached end of life will not receive new firmware, Tom’s Hardware reports. For those devices, Asus advises strong, unique login and Wi-Fi passwords. That password advice is not a confirmed fix for either vulnerability.
The exposed data allowed him to map more than 300,000 Flock-associated surveillance devices across the US, according to an October 2 report.
1 min
The standard establishes common requirements for optical links as their use expands in SI and data-center systems, according to Semiconductor Engineering.
1 min
The funding will support commercialization of connections between SI processors, with a design intended to contain optical failures without stopping computation.
